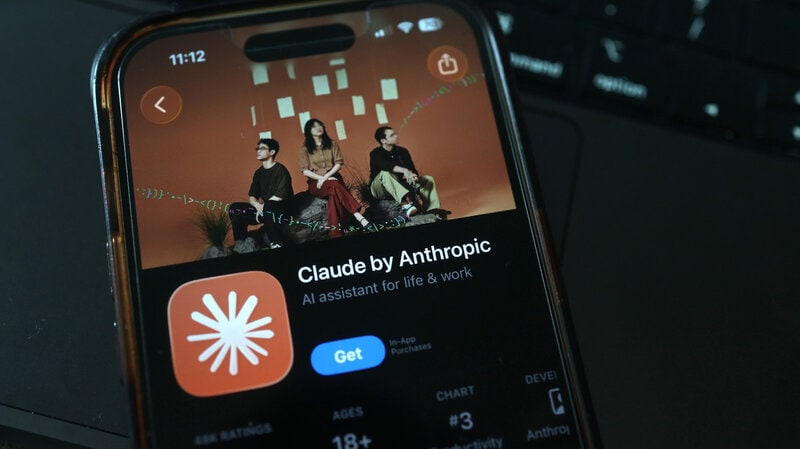
Anthropic is bringing free AI code checks to open-source projects with OSS Scanner, an opt-in service that searches software for security weaknesses before maintainers patch them. What sets it apart is cost: participating projects get recurring scans from Anthropic's top models at no cost instead of paying for a broader code-security product.
Because the reports come straight from the models, projects can check code more often but still need to confirm findings before acting on them. Claude Mythos is part of that stack, giving small maintainer teams a high-powered second look without adding staff.
At no cost, OSS Scanner gives community projects access to audits that otherwise sit in paid products like Claude Security. It turns baseline code scanning into shared infrastructure for the open-source software that underpins the Internet.
Image Credit: Michael M. Santiago / Getty Images
What Makes This Trend Stand Out
- Free AI Security
- No-cost vulnerability scanning turns advanced code audits into accessible infrastructure for under-resourced open-source teams.
- Model-led Code Review
- AI-generated security reports expand the frequency of code inspection while preserving demand for human validation and triage.
- Open-source Risk Infrastructure
- Shared security tooling for public repositories creates new platform value around protecting the software foundations used across enterprises.
Sectors Adopting This
- Cybersecurity
- Freemium AI scanning pressures traditional code-security vendors to differentiate through accuracy, workflow integration, and verified remediation.
- Open-source Software
- Community-led projects gain enterprise-grade defensive capabilities that can strengthen trust, adoption, and long-term ecosystem resilience.
- Developer Tools
- Security checks embedded into maintainer workflows signal a shift toward lightweight, recurring assurance layers built directly around code collaboration.