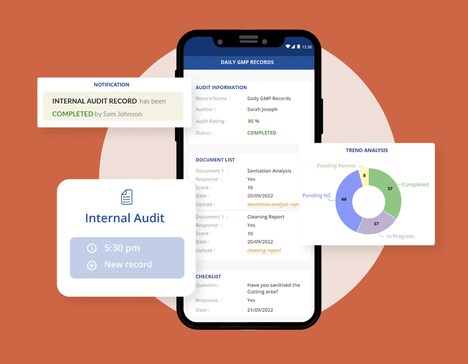
SBS CyberSecurity is expanding TRAC with Incident Response, bringing cyber incident planning, response and documentation into the company’s existing governance, risk and compliance platform. The addition keeps preparation, exercises and live incident work within the same system rather than spreading them across separate documents and tools.
Teams can start with a built-in incident response template and use tabletop exercises to work through potential scenarios before an actual event occurs. This gives organisations a structured way to define responsibilities, test their plans and record what happens during a response, with banks and credit unions among the intended users.
The update broadens TRAC from a platform focused on oversight and audit activities into a tool that can also support the practical side of incident management. Bringing planning and response into the same workflow can make it easier for teams to move from preparation to action while maintaining documentation of the process.
Image Credit: SBS CyberSecurity
Key Themes Behind This Trend
- Integrated Incident Governance
- Cybersecurity platforms are merging risk oversight with real-time response workflows, creating space for unified systems that reduce fragmentation across planning, execution, and audit documentation.
- Tabletop Exercise Automation
- Scenario-based cyber drills are becoming embedded into compliance tools, enabling more consistent preparedness testing and richer operational data before live incidents occur.
- Auditable Response Documentation
- Continuous evidence capture during cyber events is reshaping incident management, with new value emerging from response records that support compliance, learning, and accountability.
Where This Applies
- Cybersecurity Software
- Vendors are expanding beyond detection and monitoring into workflow-driven incident readiness, positioning integrated response management as a differentiator for regulated customers.
- Banking Technology
- Financial institutions require tools that connect compliance obligations with practical cyber response, opening demand for secure platforms tailored to audit-heavy operating environments.
- Governance Risk and Compliance
- GRC solutions are evolving into operational hubs, where incident planning and response capabilities transform static oversight systems into active risk management infrastructure.